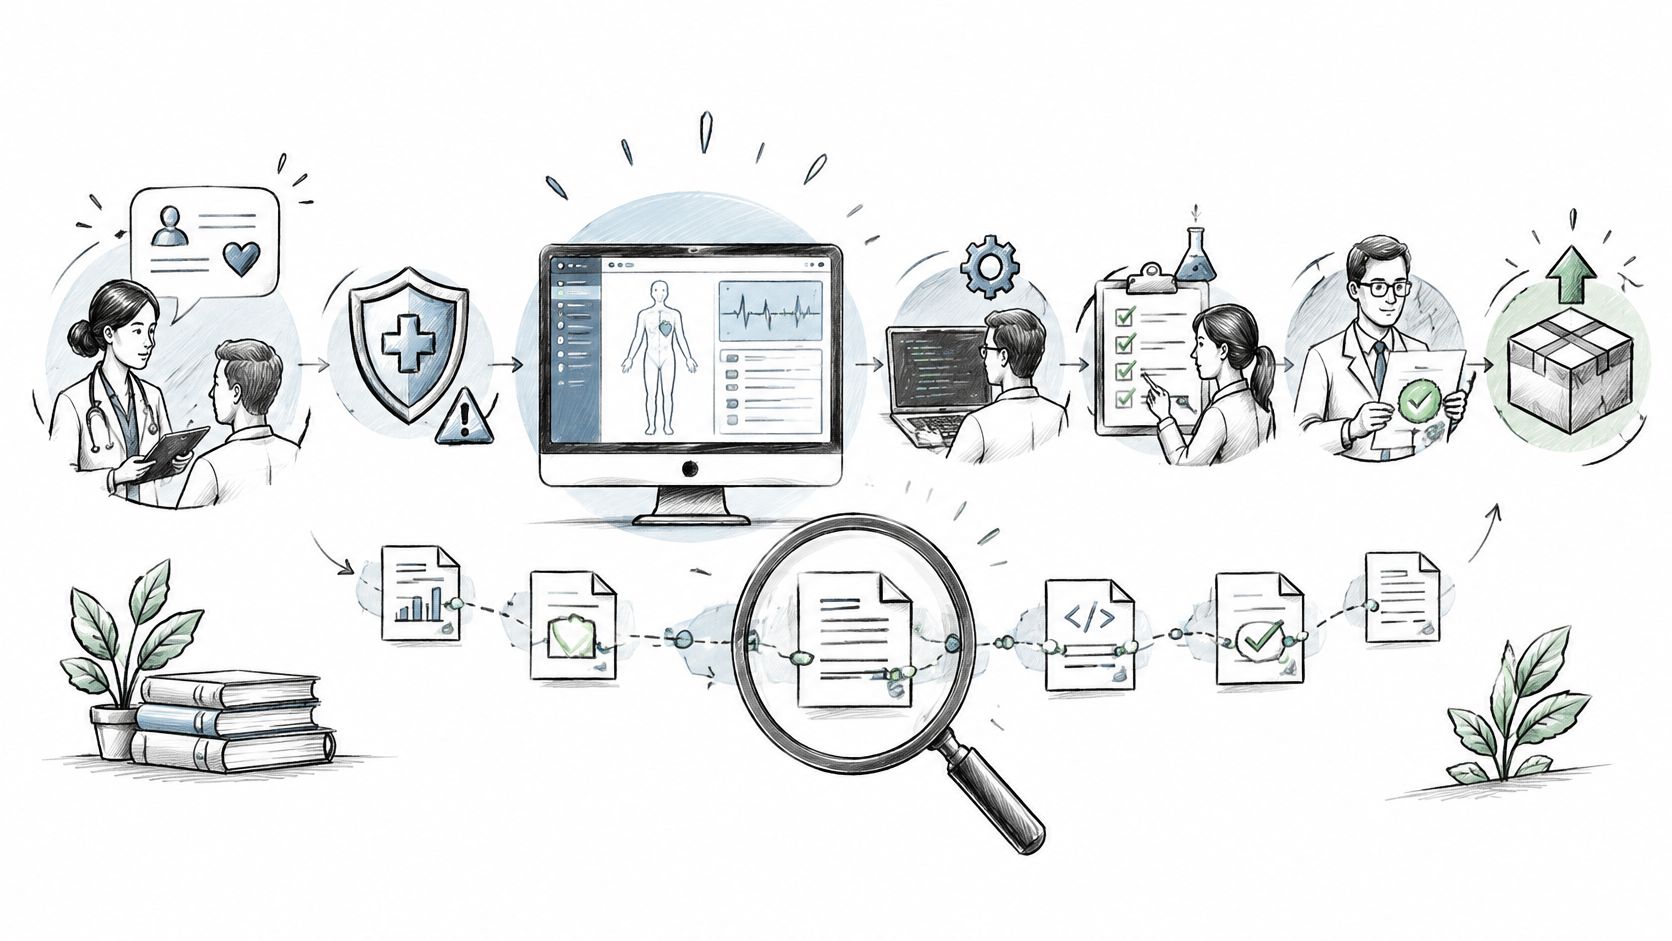
ISO 13485 Design Controls for Software Teams
ISO 13485 design controls for software teams: clause 7.3 stages, traceability, agile sprint mapping, tools and the FDA QMSR.
Read moreNov 9, 2026
Explore our blog for insights from AI strategy and solution experts covering everything from consulting and use case translation to implementation roadmaps and real-world solution building.
Showing 1–9 of 659 articles
ISO 13485 design controls for software teams: clause 7.3 stages, traceability, agile sprint mapping, tools and the FDA QMSR.
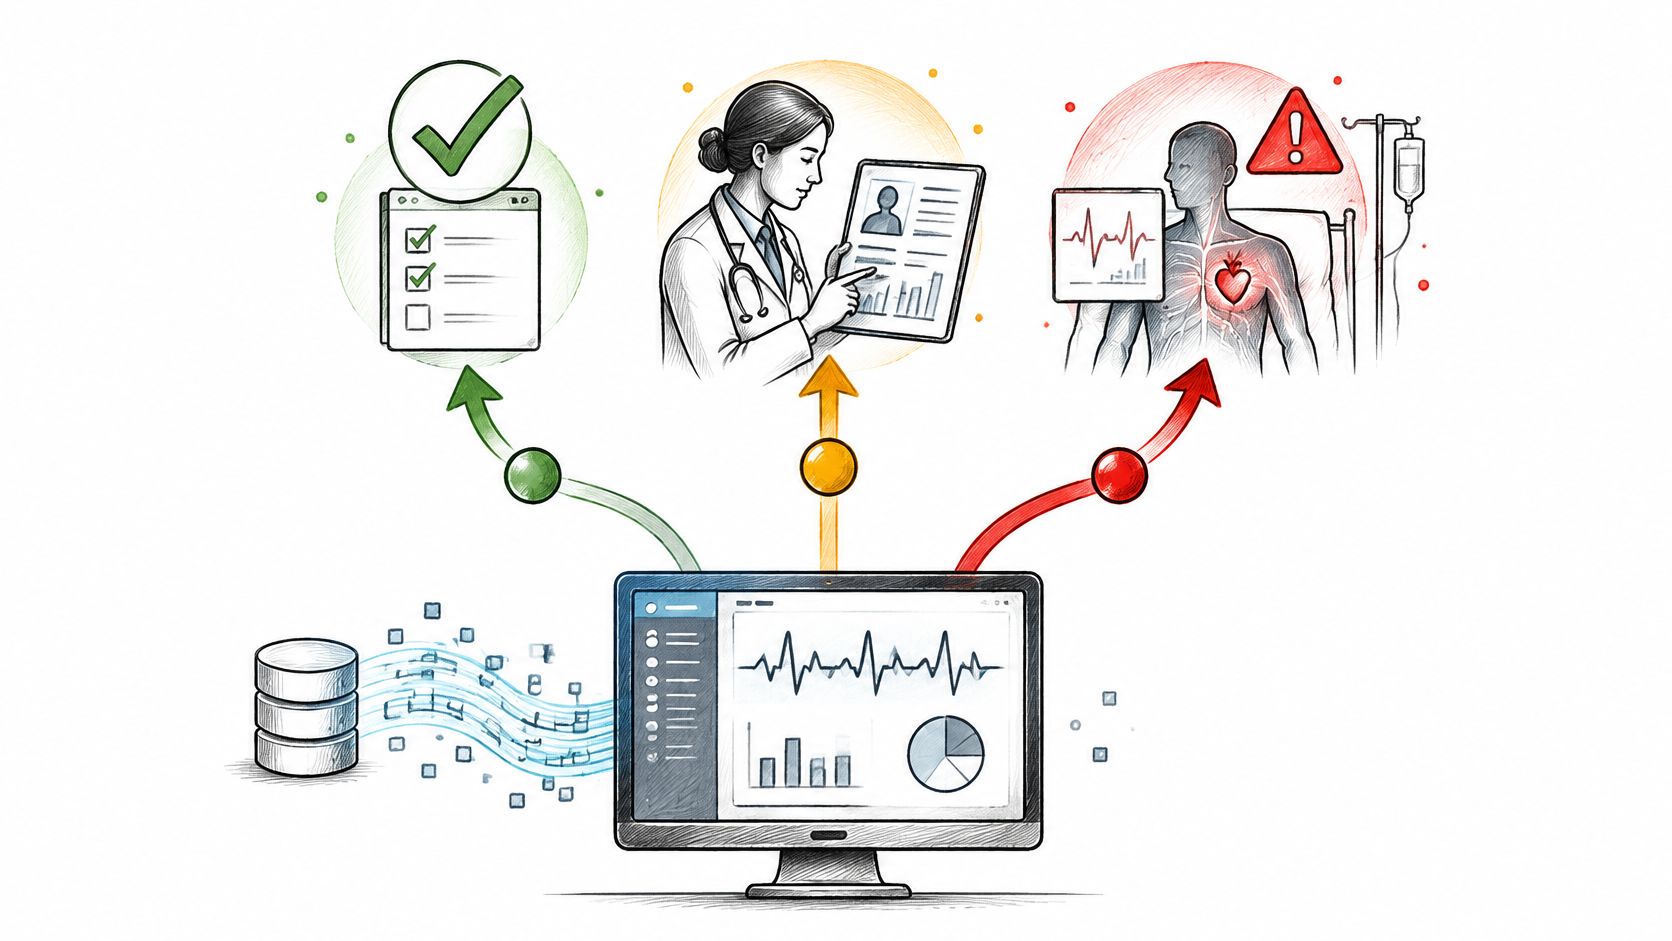
EU MDR Rule 11 explained: how Annex VIII classifies medical device software as Class I, IIa, IIb or III, with MDCG 2019-11 Rev.1 guidance.
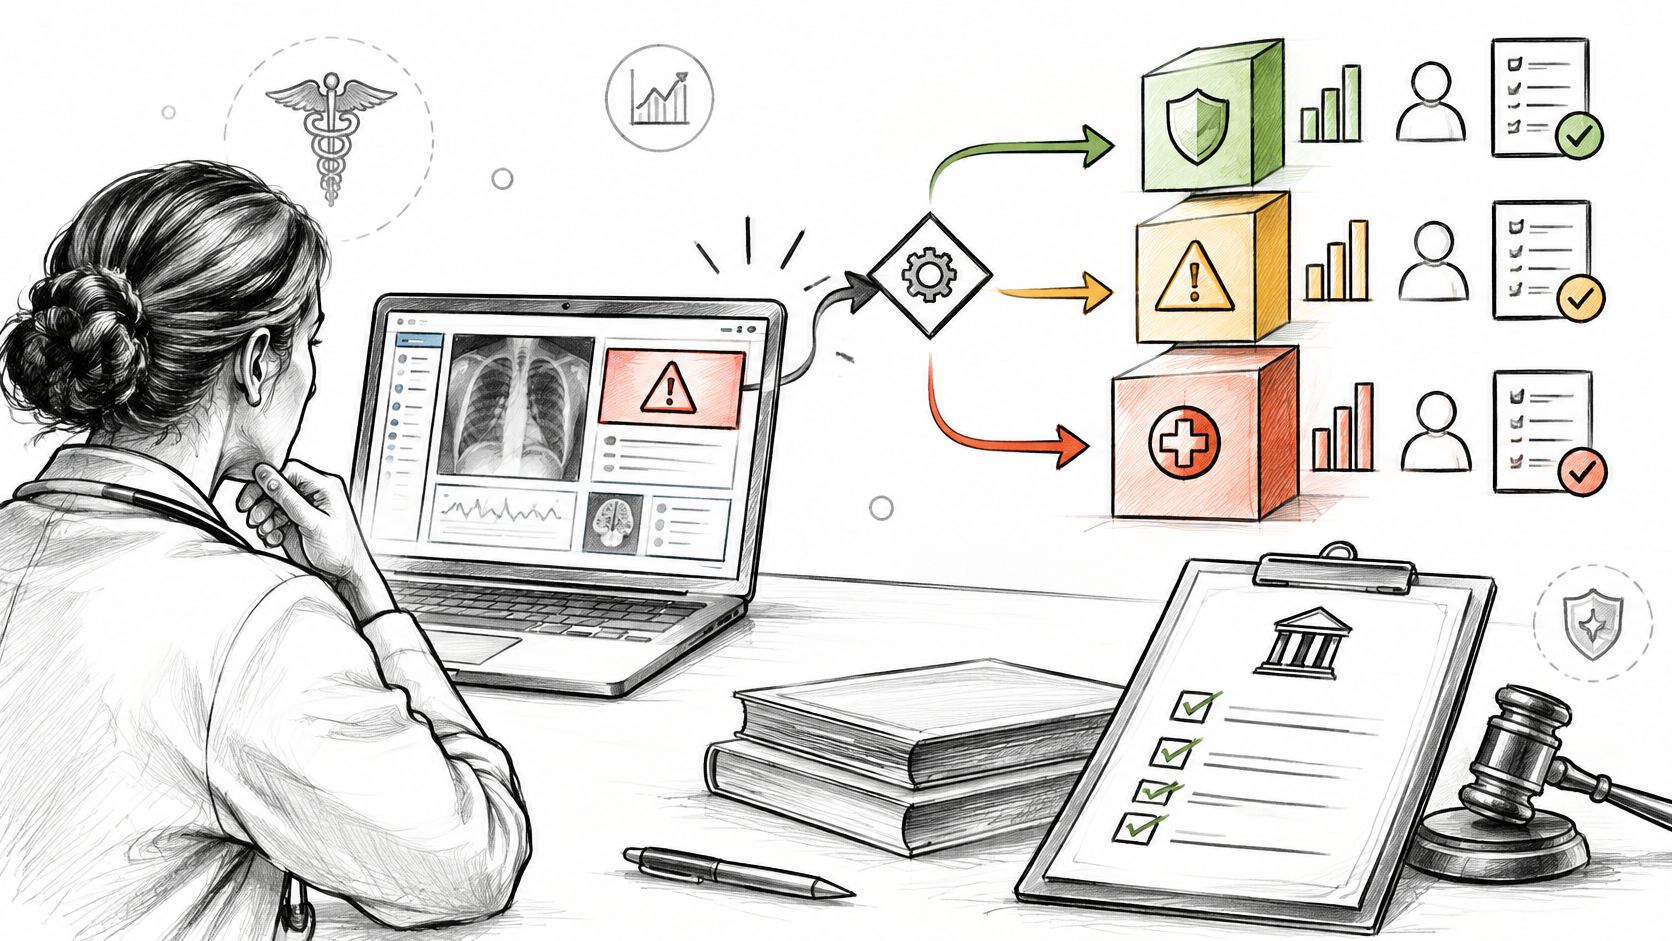
SaMD classification FDA explained: IMDRF risk categories, FDA device classes, 510(k), De Novo and PMA routes, and CDS exclusions for healthtech teams.
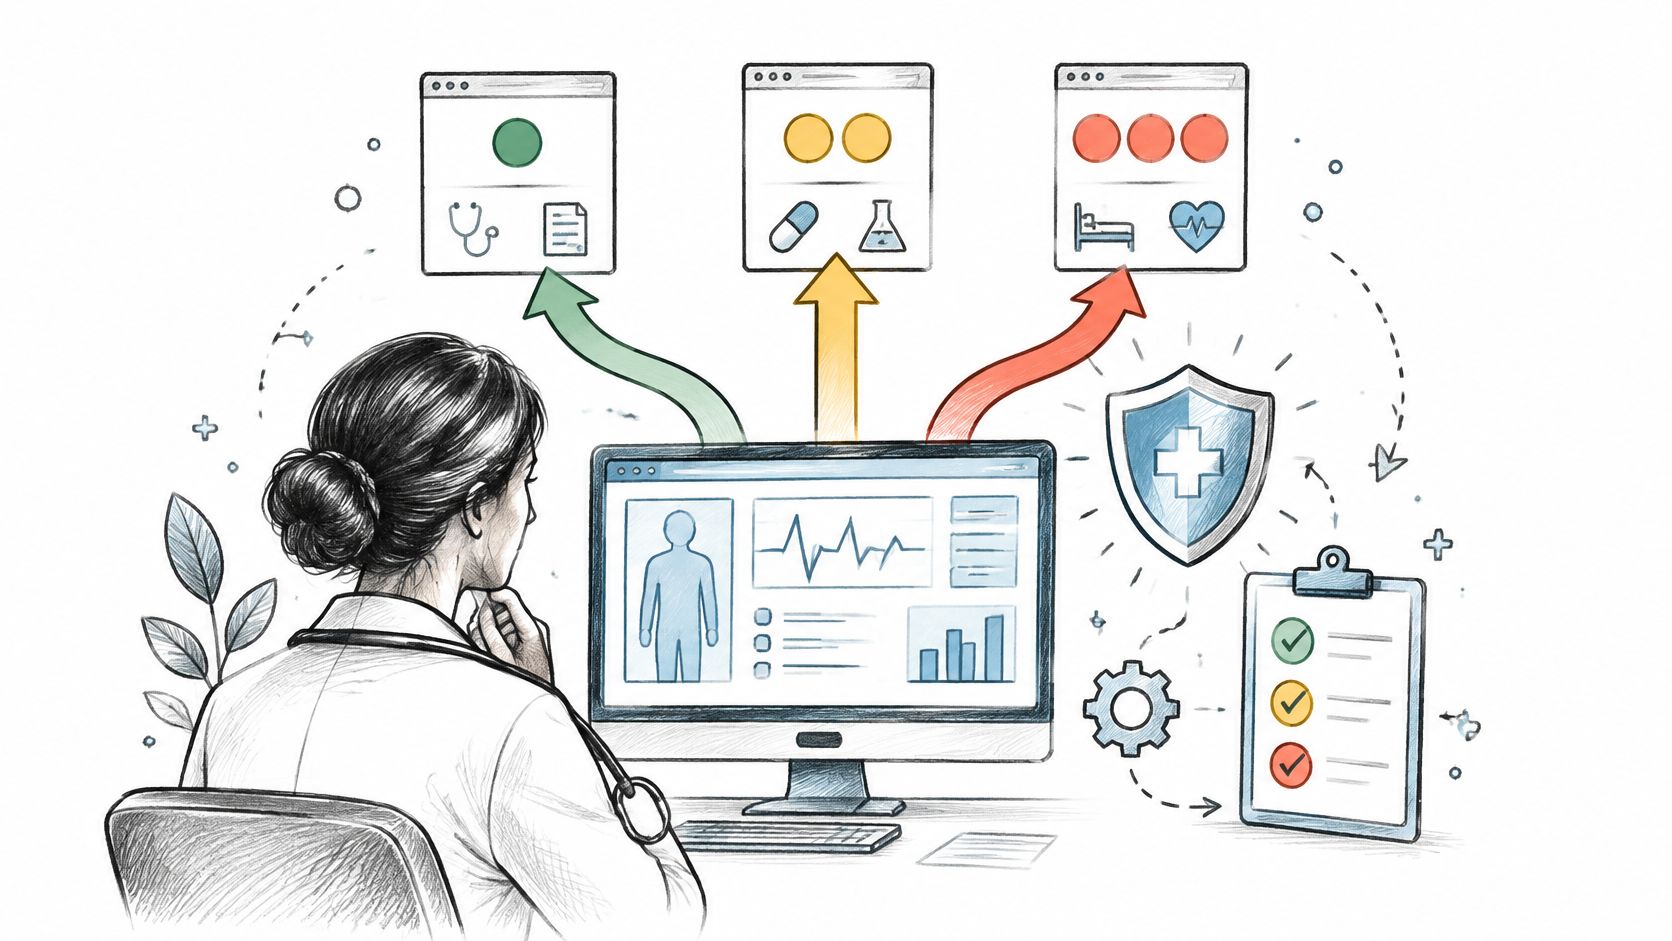
IEC 62304 software safety classification explained: how Class A, B and C are assigned, what each class requires, and what Edition 2 changes.
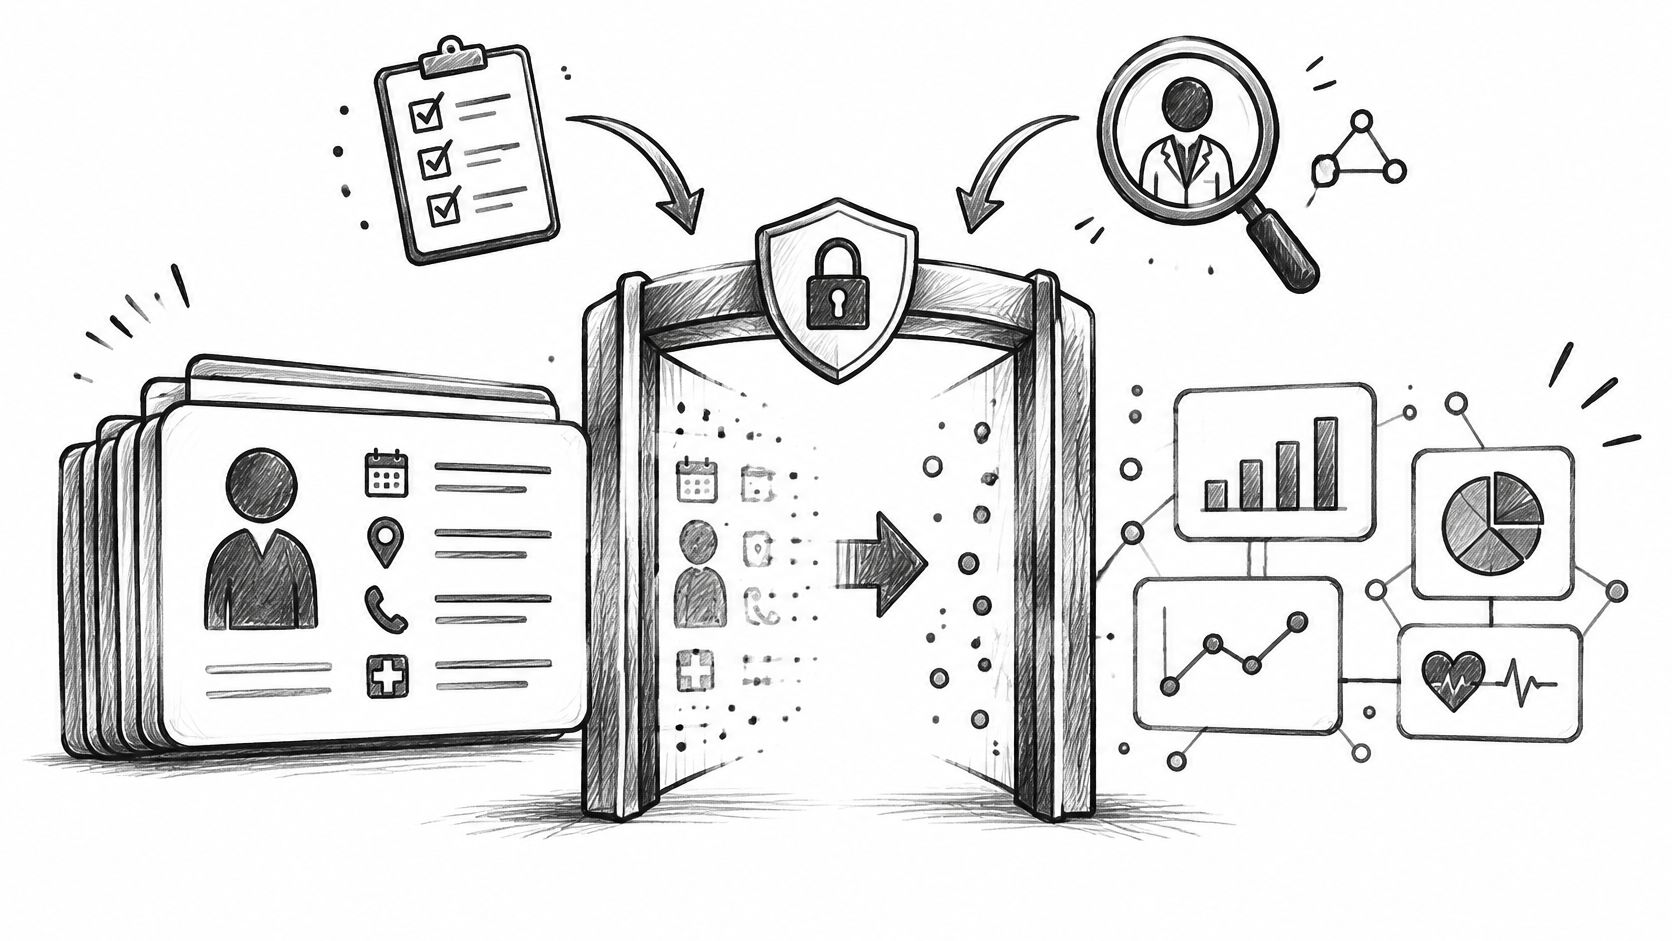
Compare PHI de-identification methods under HIPAA: Safe Harbor, Expert Determination, tokenization, free-text redaction and re-identification risk.
HITRUST vs SOC 2 for healthtech: assurance model, HITRUST e1, i1 and r2 levels, hospital buyer demands and the order to pursue them.
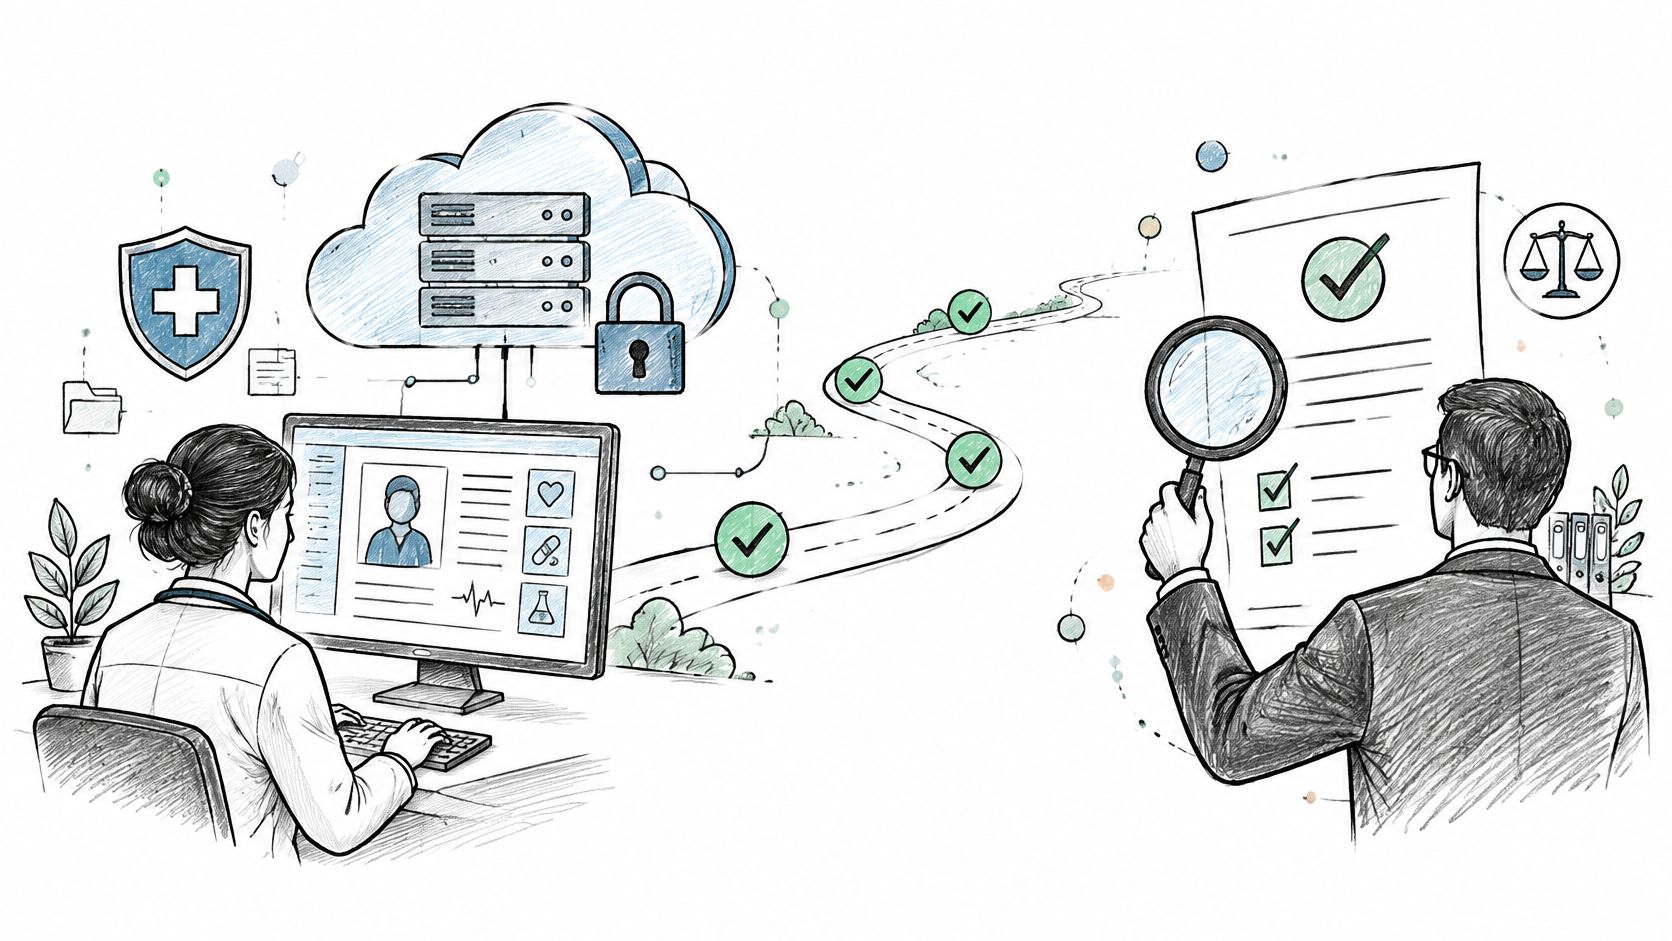
A practical roadmap to SOC 2 for HealthTech startups: Type I vs Type II, Trust Services Criteria, HIPAA overlap, and the steps to a Type II report.
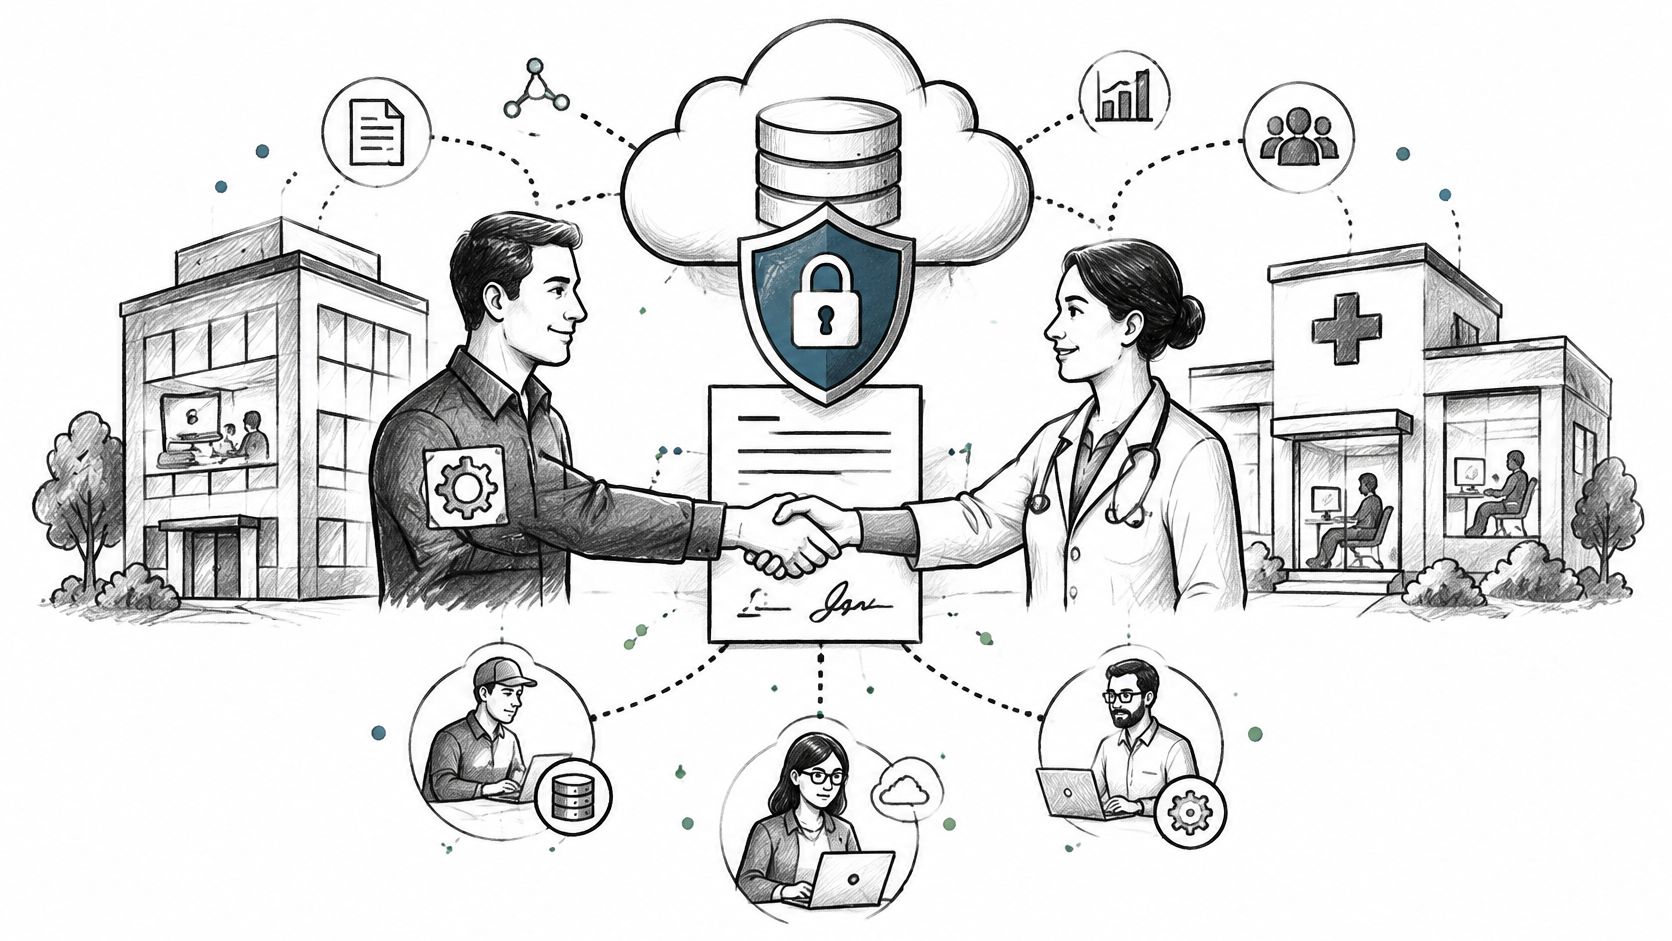
A business associate agreement for software vendors: when PHI access makes you a business associate, required clauses, subcontractors, and a checklist.
HIPAA Compliant App Development Checklist for engineering leads: ten controls mapped to the Security Rule, with evidence, tests and owners.
Connect with our team to explore how AI expertise can transform your business.