AI in Healthcare
HIPAA-Compliant AI: How to Use LLMs With PHI Safely
How to build HIPAA-compliant AI: when LLM providers need a BAA, data minimization, de-identification, audit controls and a reference architecture.
October 16, 2026Read more
Secure healthcare AI solutions help enterprise providers protect sensitive data, support compliance, streamline workflows, and deliver reliable AI-powered care.
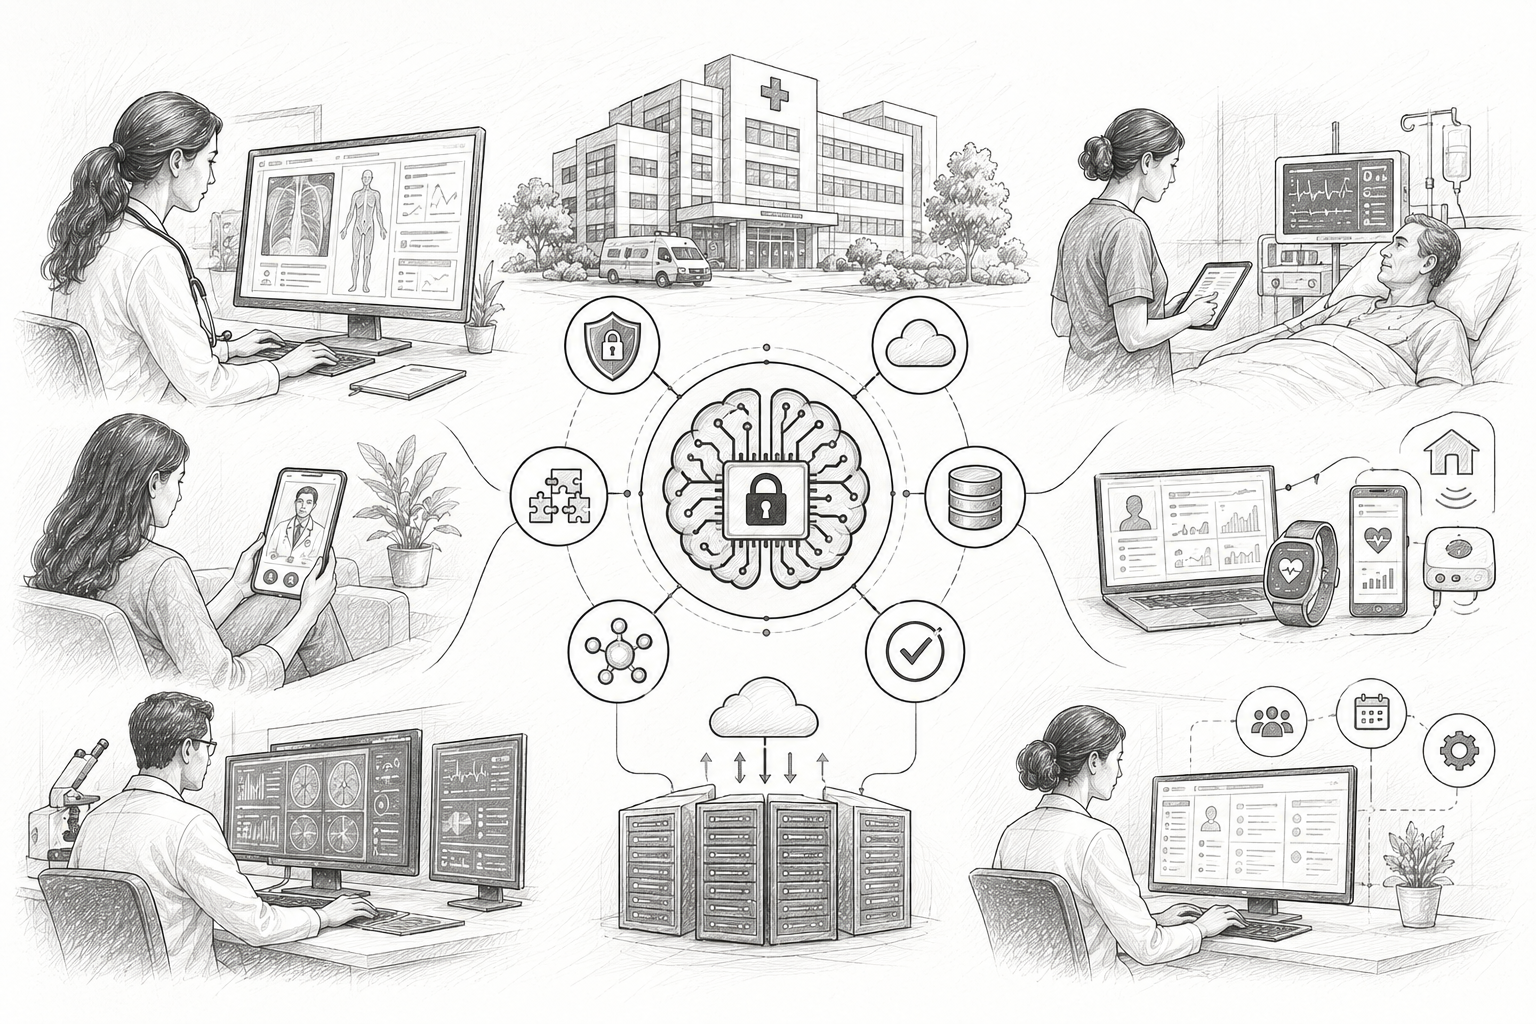
Artificial intelligence is becoming an increasingly important part of modern healthcare. Healthcare organizations are using AI to support clinical decisions, automate repetitive processes, improve patient engagement, analyze medical data, and optimize operational workflows.
For enterprise providers, however, adopting AI is not simply a matter of selecting a model or purchasing an AI-powered application. Large healthcare organizations operate complex environments that include electronic health records, diagnostic systems, patient portals, medical devices, administrative platforms, and numerous third-party applications.
These systems process sensitive patient information and support critical healthcare workflows. As a result, AI solutions must be designed around security, interoperability, reliability, and responsible use from the beginning.
This makes the development of healthcare AI solutions fundamentally different from implementing general-purpose AI applications.
Enterprise providers need AI platforms that can integrate with existing infrastructure, protect sensitive information, support clinical workflows, and scale without compromising performance or compliance.
A security-first approach allows healthcare organizations to explore AI innovation while maintaining the trust of patients, clinicians, and other stakeholders.
A small AI pilot and an enterprise healthcare AI platform have very different requirements.
A pilot may involve a limited dataset, a small group of users, and a single workflow. Enterprise deployment can involve thousands of users, multiple facilities, large patient populations, and integration with numerous systems.
This creates several challenges.
Enterprise healthcare providers often operate a combination of modern cloud platforms and legacy systems. AI applications need to work within this environment rather than exist as isolated tools.
AI systems may process protected health information, clinical notes, diagnostic results, and other sensitive data. Strong controls are required throughout the data lifecycle.
When AI contributes to clinical workflows, organizations need mechanisms for validation, monitoring, human oversight, and accountability.
A solution that works effectively in one department may need significant architectural changes before it can support multiple hospitals, specialties, or locations.
Healthcare organizations need to understand the regulatory implications of the specific AI application, particularly when software influences diagnosis, treatment, monitoring, or other clinical decisions.
These considerations make architecture and planning just as important as the AI model itself.
A secure AI healthcare environment should protect information and manage risks across the complete AI lifecycle.
This begins with the underlying data architecture.
Healthcare data should be protected while it is stored, transmitted, and processed. Access should also be controlled according to user roles and organizational requirements.
A mature architecture typically includes:
Identity and access management
Data encryption
Secure APIs
Network protection
Audit logging
Data governance
Continuous monitoring
Backup and recovery mechanisms
Security should also extend to the AI models and applications themselves.
Organizations need to understand where models are hosted, what information they access, how outputs are generated, and who can use those outputs.
The goal is not simply to create a secure application. It is to create an environment where AI can operate safely within the broader healthcare technology ecosystem.
AI depends on data, but healthcare data is rarely available in one clean, standardized environment.
Patient information can exist across EHR platforms, laboratory systems, imaging applications, medical devices, patient engagement platforms, and operational databases.
This fragmentation can make enterprise AI implementation difficult.
Before deploying advanced AI, organizations should evaluate:
Incomplete, duplicated, outdated, or inconsistent information can affect AI performance.
AI applications need appropriate access to the information required for their specific use case.
Systems should exchange information through reliable and secure interfaces.
Organizations need clear policies covering data ownership, access, retention, quality, and usage.
A strong data foundation makes it easier to develop reliable AI applications while reducing integration complexity.

Many organizations start with a single AI use case.
A clinical documentation assistant, predictive analytics platform, or patient-facing AI tool may demonstrate value within a limited environment. The challenge begins when leadership wants to expand that capability across departments or facilities.
Scaling requires a different architectural mindset.
Instead of creating separate AI applications for every department, organizations can establish reusable infrastructure that supports multiple use cases.
This may include:
Shared data services
Common authentication
Reusable healthcare APIs
Centralized monitoring
Standardized model deployment
Common governance processes
Scalable cloud infrastructure
This approach makes enterprise healthtech more adaptable.
New AI applications can be introduced without rebuilding the underlying technology environment each time.
Security is only one part of responsible enterprise AI. Organizations also need a structured approach to AI governance.
AI governance establishes how AI systems are selected, developed, validated, deployed, monitored, and eventually retired.
A useful governance framework can address:
Model validation
Data quality
Privacy
Security
Bias and fairness
Explainability
Human oversight
Performance monitoring
Incident management
The NIST AI Risk Management Framework is one example of a voluntary framework designed to help organizations incorporate trustworthiness considerations into the design, development, deployment, and evaluation of AI systems.
For healthcare providers, governance becomes particularly important when AI outputs can influence clinical decisions.
A governance process should define who is responsible for validating a model, who can approve deployment, how performance is measured, and what happens when the system produces unexpected results.
This creates accountability around AI rather than treating the technology as a standalone application.
Enterprise AI requires expertise across several areas at once.
Organizations may need support with data engineering, AI development, cloud infrastructure, system integration, security, workflow design, and regulatory considerations.
Specialized healthcare AI services can help organizations address these requirements through a coordinated approach.
Depending on the use case, this can include:
Evaluating existing systems, data, workflows, and organizational readiness.
Designing AI-powered applications around specific clinical or operational requirements.
Connecting AI applications with existing healthcare platforms and workflows.
Deploying and integrating appropriate models while establishing monitoring and evaluation processes.
Ensuring AI supports existing clinical and administrative processes rather than creating additional complexity.
The objective is to make AI useful within the healthcare environment, not simply technically impressive.
Enterprise AI projects often require coordination between clinical teams, IT departments, security professionals, data engineers, product teams, and leadership.
A specialized healthtech engineering partner can help bring these requirements together.
The value extends beyond software development.
An experienced engineering team can help organizations evaluate system architecture, identify integration requirements, design secure infrastructure, and translate healthcare workflows into scalable technology.
Before making significant AI investments, organizations can also develop a custom AI strategy report that evaluates:
Existing technology infrastructure
AI readiness
Data availability
Integration requirements
Security considerations
High-value use cases
Implementation priorities
Long-term scalability
This provides decision-makers with a clearer view of where AI can create value and what needs to be addressed before implementation.
A strategic approach helps prevent organizations from accumulating disconnected AI tools that cannot communicate with one another.
Healthcare AI is increasingly being used across different stages of the patient journey.
For example, AI may support patient intake before an appointment, assist clinicians during consultation, analyze diagnostic information, and help coordinate follow-up care.
Each stage creates different security and governance requirements.
A patient-facing AI application needs strong privacy and identity controls.
A clinical decision-support system requires validation and appropriate human oversight.
An AI application used for medical diagnosis or monitoring may also fall within a regulated medical software framework depending on its intended use and jurisdiction.
This is where SaMD solutions become relevant.
Software that performs medical functions can require additional consideration around clinical safety, validation, risk management, and regulatory compliance.
Organizations should therefore assess the intended function of each AI application before deciding how it should be developed, validated, and deployed.
Secure AI does not mean removing people from the process.
In healthcare, human oversight remains particularly important when AI outputs may affect patient care.
AI systems should make it clear when an output is generated by a model and provide healthcare professionals with enough context to evaluate that output.
Effective human oversight can include:
Clinician review
Confidence indicators
Escalation mechanisms
Audit trails
Override capabilities
Performance monitoring
This creates a collaborative model in which AI handles analysis or repetitive tasks while healthcare professionals retain responsibility for decisions that require clinical judgment.
The right balance depends on the specific application, risk level, and intended use.
Enterprise healthcare organizations should treat AI security as an ongoing process rather than a one-time implementation task.
As models, data sources, applications, and user groups change, new risks can emerge.
A scalable security strategy should therefore include continuous:
Vulnerability assessment
Access review
Model monitoring
Data quality evaluation
Compliance assessment
Security testing
Incident response
Organizations should also maintain documentation throughout the AI lifecycle.
This makes it easier to understand how a system was developed, what data it uses, how it has been validated, and how its performance changes over time.
Such documentation becomes especially valuable when AI systems expand into new clinical or operational environments.
Enterprise providers do not need to transform every healthcare workflow at once.
A more sustainable approach is to identify a small number of high-value use cases, establish secure foundations, and then expand gradually.
A practical sequence can include:
Assess: Understand existing infrastructure, data, workflows, and risks.
Prioritize: Select AI opportunities based on clinical value, operational impact, feasibility, and risk.
Design: Establish the architecture, security controls, integration requirements, and governance model.
Validate: Test the AI application within a controlled environment.
Deploy: Introduce the solution into the appropriate workflow with human oversight.
Monitor: Continuously evaluate performance, security, user adoption, and outcomes.
Scale: Expand successful applications across additional departments or facilities.
The future of enterprise healthcare will increasingly depend on intelligent technologies that can operate securely within complex healthcare environments.
Successful healthcare AI solutions require more than powerful models. They require reliable data, secure infrastructure, interoperability, strong AI governance, appropriate human oversight, and a clear strategy for scaling.
By combining secure AI healthcare architecture with specialized healthcare AI services, compliant SaMD solutions, and support from an experienced healthtech engineering partner, organizations can build AI capabilities that are designed for real healthcare environments.
A custom AI strategy report can provide the starting point by helping healthcare leaders assess readiness, identify high-value opportunities, understand technical requirements, and establish priorities for responsible AI adoption.
The organizations that approach AI as an enterprise capability rather than a collection of disconnected tools will be better positioned to build secure, scalable, and sustainable digital healthcare ecosystems.
Healthcare AI solutions are software applications that use artificial intelligence to support clinical care, diagnostics, patient engagement, healthcare operations, and decision-making.
AI governance is the framework used to manage how AI systems are selected, developed, validated, deployed, monitored, and updated. It helps establish accountability, transparency, security, and responsible AI practices.
A healthtech engineering partner can help organizations design AI architecture, integrate healthcare systems, develop secure applications, address interoperability requirements, and scale AI across complex healthcare environments.
A custom AI strategy report helps organizations evaluate their technology and data readiness, identify high-value AI opportunities, understand implementation requirements, and establish a practical roadmap for secure and scalable AI adoption.
How to build HIPAA-compliant AI: when LLM providers need a BAA, data minimization, de-identification, audit controls and a reference architecture.
Practical data migration planning guide for healthcare teams. Scope, mapping, compliance, validation, cutover and rollback decisions explained end to end.
Smart on FHIR guide for healthtech engineers. Learn the OAuth 2.0 launch model, scope syntax, backend services, and US regulatory requirements.
Connect with our team to explore how AI expertise can transform your business.