AI Integration
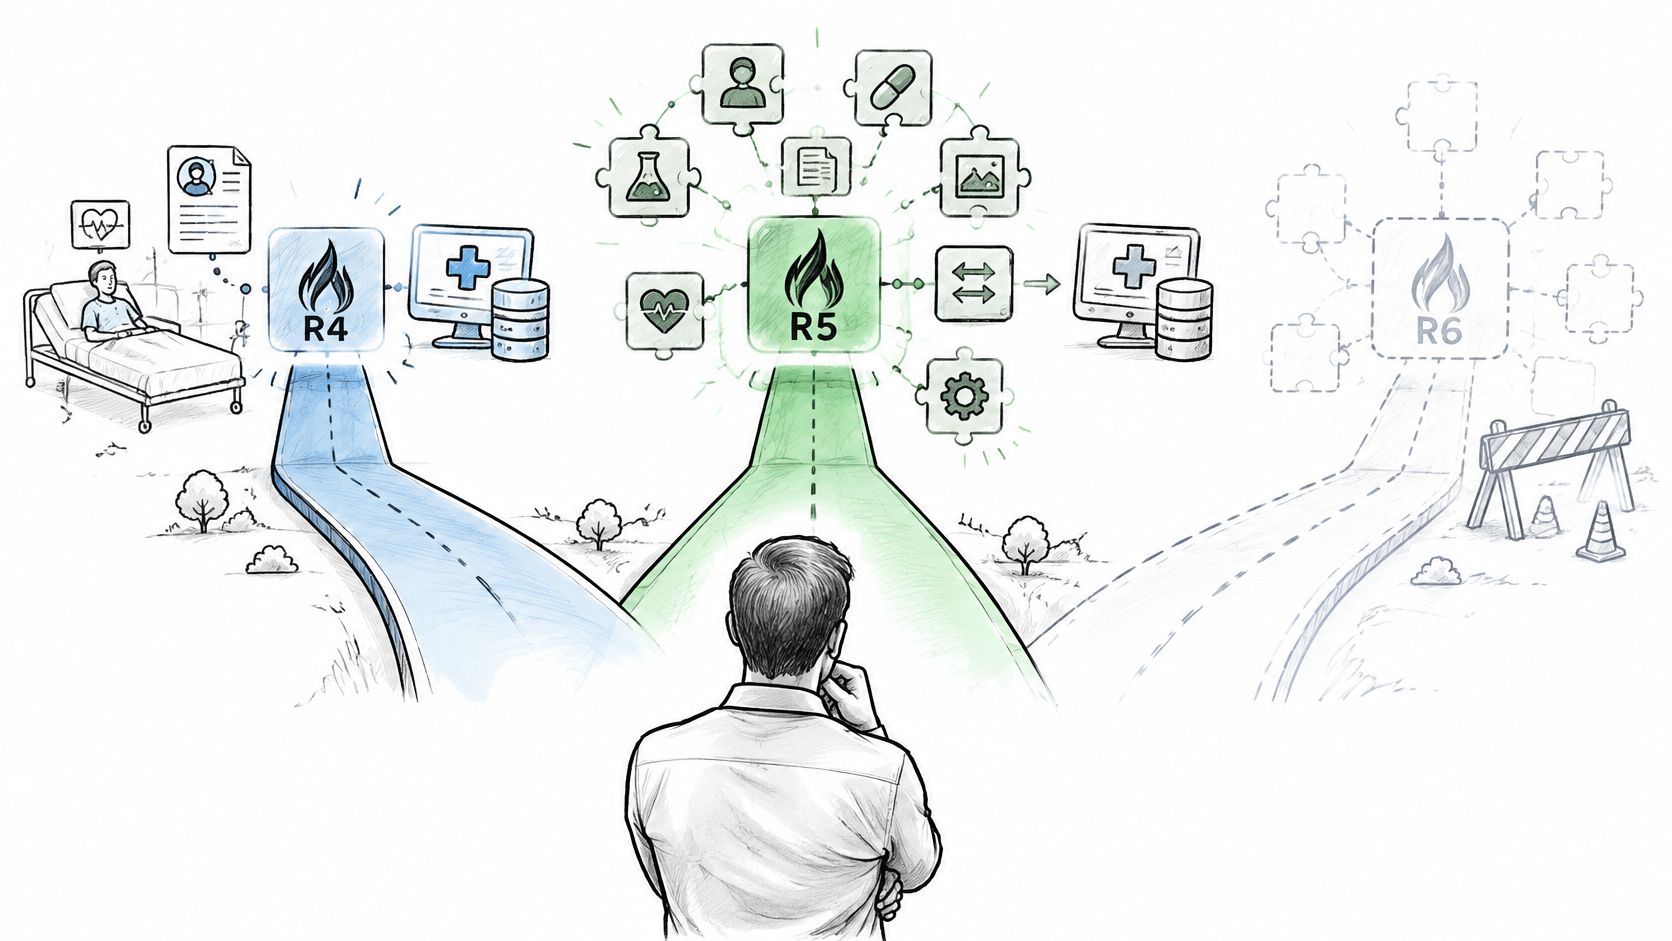
FHIR R4 vs R5 (and R6): Which Version Should You Build On?
FHIR R4 vs R5 compared for US EHR integration: maturity, breaking changes, US Core and vendor support, R6 status, and a build decision.
October 27, 2026Read more
How to govern AI in healthcare: governance models, risk management, validation and monitoring, plus the FDA, HIPAA, Section 1557 and HTI-1 rules that apply.

Healthcare AI governance is how an organization decides which AI tools it uses, checks that they are safe, fair and effective, and keeps them under control after go-live. Compliance is the part of that work that answers to law and regulators: FDA rules for medical devices, HIPAA for patient data, nondiscrimination rules and certification requirements for health IT. This guide explains the main building blocks, the rules that shape them and which of our articles to read next.
Expectations are rising from accreditors as well as regulators. In September 2025, the Joint Commission and the Coalition for Health AI released guidance on the responsible use of AI in healthcare that covers governance, privacy and transparency, data security, quality monitoring, safety event reporting, risk and bias assessment, and staff education, according to the Joint Commission.
| Your goal | Read |
|---|---|
| Choose a governance model for your organization | Healthcare AI governance models |
| Compare governance tooling | AI governance platforms for healthcare teams |
| Manage patient safety risk from clinical AI | Clinical AI risk management Responsible AI in clinical practice |
| Make AI outputs understandable to clinicians | Explainable AI in clinical decision making |
| Turn ethics principles into checks | Ethical AI in healthcare |
| Plan FDA submissions for AI devices that will change over time | Predetermined change control plans |
| Use large language models with patient data | HIPAA-compliant AI |
| Build HIPAA compliance into software and cloud systems | HIPAA compliance for software development HIPAA compliance on AWS |
| Prepare for a HIPAA audit | HIPAA compliance audit |
| Secure AI systems and deployments | Securing AI systems in healthcare Building secure healthcare AI solutions |
| Build compliance into engineering and automate it | Compliance engineering in HealthTech Healthcare compliance automation |
| Understand AI rules outside healthcare and use AI for compliance work | AI regulatory compliance How AI helps with compliance work |
| Check whether your organization is ready for AI | AI readiness framework for healthcare organizations |
| Building block | What it covers |
|---|---|
| Inventory | Every AI tool in use, including features inside vendor products, with an owner for each |
| Intake and risk tiering | A review before adoption, with deeper checks for tools that affect diagnosis, treatment or access to care |
| Validation | Testing on local data before go-live, including performance across patient groups |
| Monitoring | Tracking performance, drift, errors and safety events after deployment |
| Transparency | Clear information for clinicians and, where appropriate, patients about how a tool works and its limits |
| Security and privacy | Access control, logging, data minimization and contracts with vendors that handle patient data |
| Retirement | Criteria and a process for updating or switching off tools that no longer perform |
Start with an inventory, because most organizations already use more AI than they think, much of it inside vendor products. Set up a small cross-functional committee with clinical, IT, security, legal and quality members, agree on risk tiers, and require local validation for high-risk tools. Then build monitoring and incident reporting into daily operations, train staff on what AI can and cannot do, and review the program at least yearly as rules change.
If you are building AI products that must meet these requirements, see our healthcare engineering services and SaMD solutions.
Healthcare AI governance combines an inventory, risk-based review, validation, monitoring and transparency with the rules that apply: FDA, HIPAA, nondiscrimination requirements and health IT certification. Start with the four core articles above, use the goal table to go deeper, and treat governance as an ongoing operating process rather than a one-time approval.
If you want help setting up AI governance or building compliant AI products, book a consultation with Ekipa's HealthTech engineers.
The policies, roles and processes an organization uses to decide which AI tools to adopt and to keep them safe, fair and effective over time.
Typically clinical leaders, IT, information security, privacy and legal, quality and patient safety, and data science, with a named chair.
No. Only software that meets the definition of a medical device needs FDA oversight. Many administrative tools do not, but they still need governance.
Covered entities must make reasonable efforts to identify decision support tools that use protected characteristics as inputs and to mitigate the risk of discrimination.
Continuously for key performance and safety signals, and formally at least once a year or whenever the tool, its data or its use changes.
FHIR R4 vs R5 compared for US EHR integration: maturity, breaking changes, US Core and vendor support, R6 status, and a build decision.
Learn what drives EHR integration cost, from FHIR and HL7 scope to security review and upkeep, plus a checklist to build a reliable estimate.

How home health, hospice, SNF and senior living software works: core systems, EVV and assessment rules, value-based payment, interoperability and where AI helps.
Connect with our team to explore how AI expertise can transform your business.